Restricted access
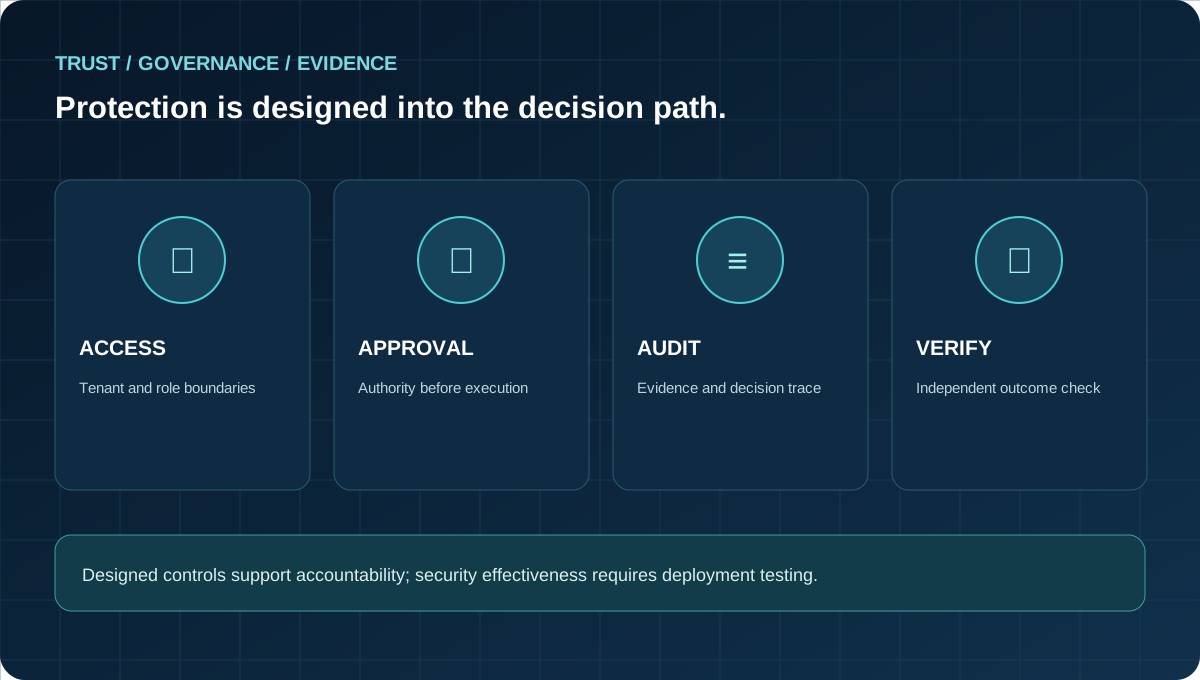
Role and tenant boundaries are designed to limit who can view information or initiate action.
PLATFORM / GOVERNANCE / PROTECTION
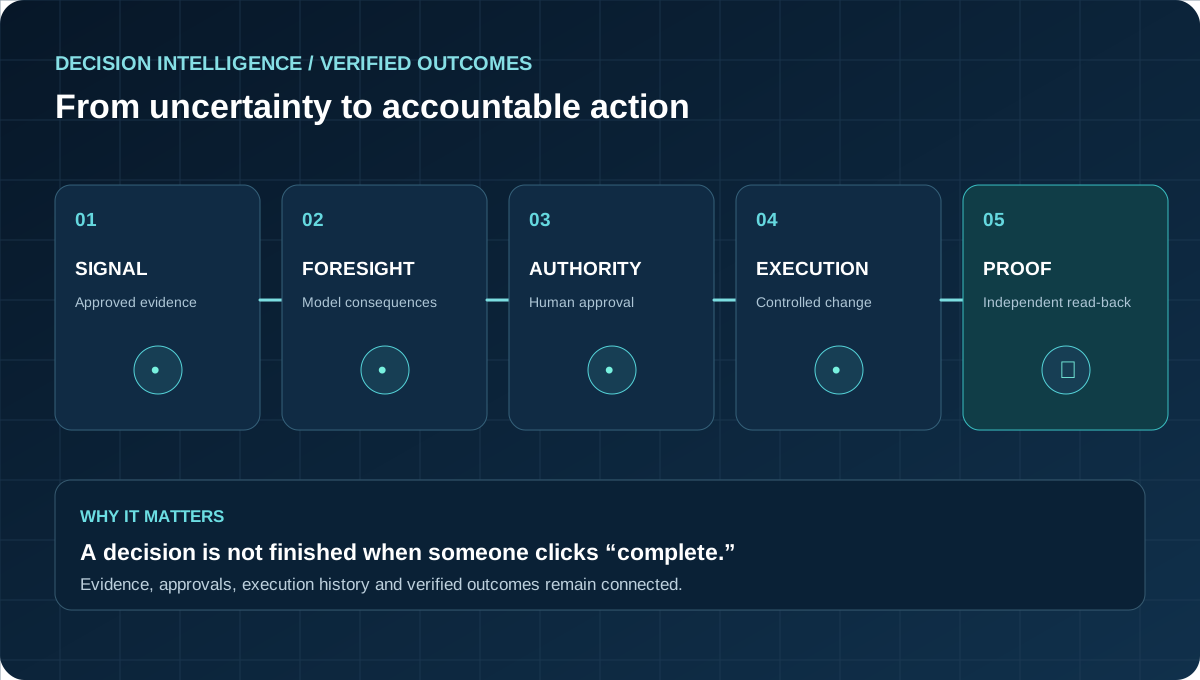
Knowing what should happen is only the beginning. Ceryvra is designed to connect the reasoning behind a decision with the people authorized to approve it, the controls governing execution and the evidence showing whether it worked.
Illustrative architecture — not a live product screenshot.
THE DECISION GENOME + QEP + EFAR
The Decision Genome preserves context, evidence, rationale and authorization. QEP and EFAR are designed to coordinate controlled action, recovery and independent outcome verification.
The goal is a traceable record—not just that work was requested or completed, but what changed, who approved it and what evidence confirms the result.
Illustrative architecture — not a live product screenshot.
PROTECTION / AUDITS / APPROVALS
Ceryvra's architecture centers on role-based access, tenant boundaries, evidence obligations, authorization checkpoints and auditable histories. These safeguards are designed to help teams act responsibly while giving leaders a clearer record for oversight and review.
Role and tenant boundaries are designed to limit who can view information or initiate action.
Consequential actions require appropriate authority, supporting evidence and traceable decisions.
Preserve the decision history and independently check whether the intended change occurred.
These are design objectives. Production security and operational effectiveness require integration, testing and acceptance.